Corvus AWPG
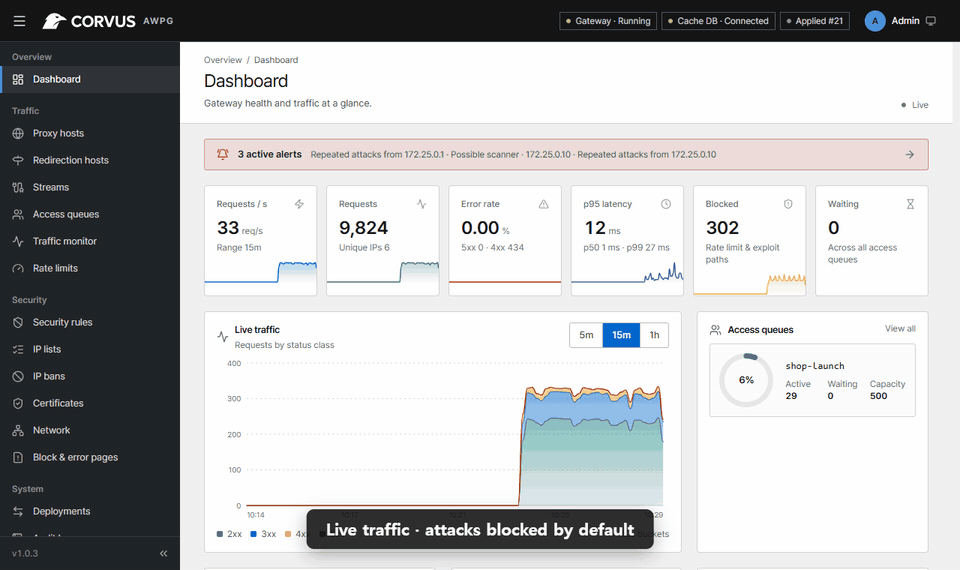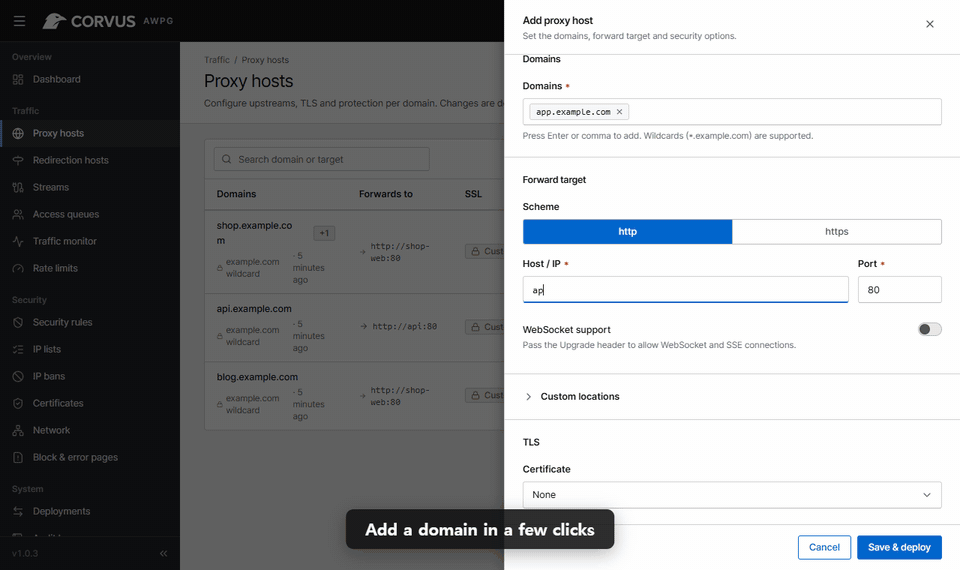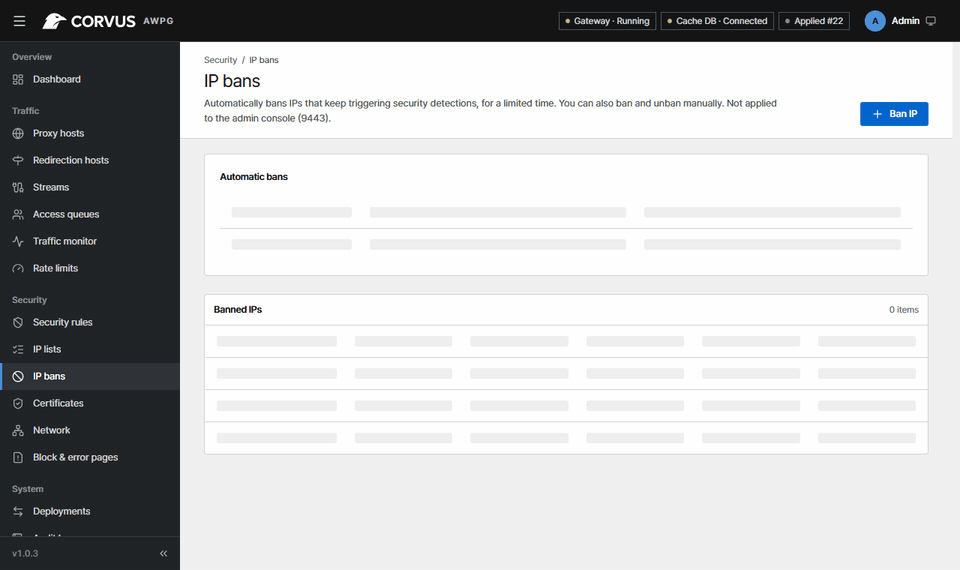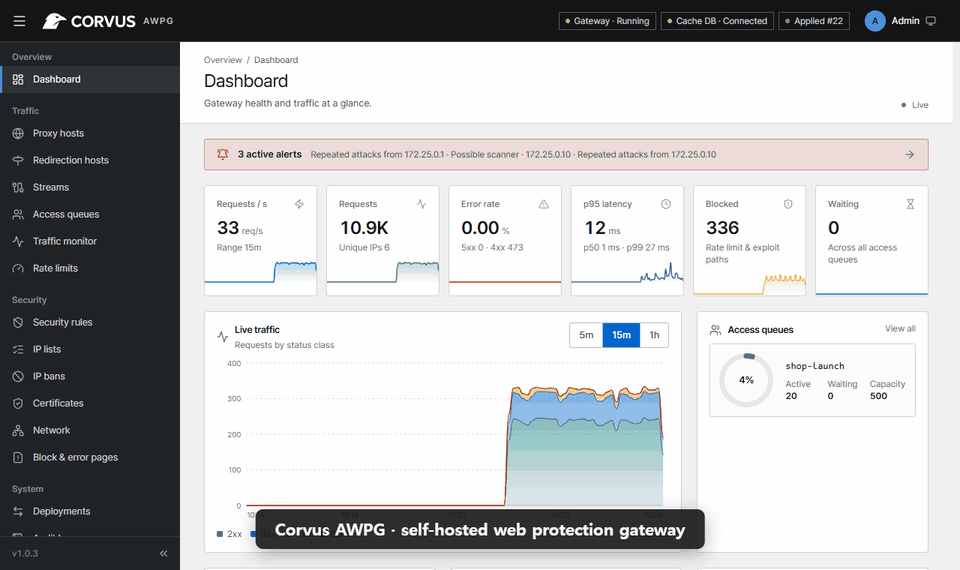
Corvus is a self-hosted gateway that sits in front of your web services. It is as easy to run as Nginx Proxy Manager (domains, forwarding and free SSL in a few clicks), and it also watches, protects and controls the traffic that passes through it. Everything runs on your own server; no traffic goes to a third-party cloud.
-
One container, one
docker-compose.yml, and a browser. -
Import proxy hosts, certificates, streams and access lists. NPM itself is not changed.
-
Attack blocking works the moment you add a host. Rules, bans and challenges are there when you need them.
-
Admit visitors up to your capacity during a launch or a flash sale and queue the rest fairly.
What you get
| Proxy & TLS | Proxy hosts, custom locations, redirections, TCP/UDP streams, Let's Encrypt certificates with automatic renewal and saved DNS credentials, what unknown hosts get: 404, closed connection or a redirect |
| Security | Known attack patterns blocked by default, security rules, IP and User-Agent lists, browser challenge and "under attack" mode, automatic bans |
| Access queue | Capacity-based waiting room for traffic spikes |
| Monitoring | Live traffic, request logs and security events, alerts to Slack, Discord, Teams, Telegram and more |
| Operations | Every change is tested and versioned, backup & restore, roles, MFA and SSO |
Safe defaults
You don't need to write a single rule to get started. Basic attack detection is on for every new host, and every advanced option stays optional.